iptraf-ng
Share on:
Enter Your Mastodon Instance
Copy the link below to share to Mastodon
https://terminaltrove.com/iptraf-ng/
A console-based low-level packet and IP traffic monitoring program.
Script Preview
Review this script before executing in your terminal.
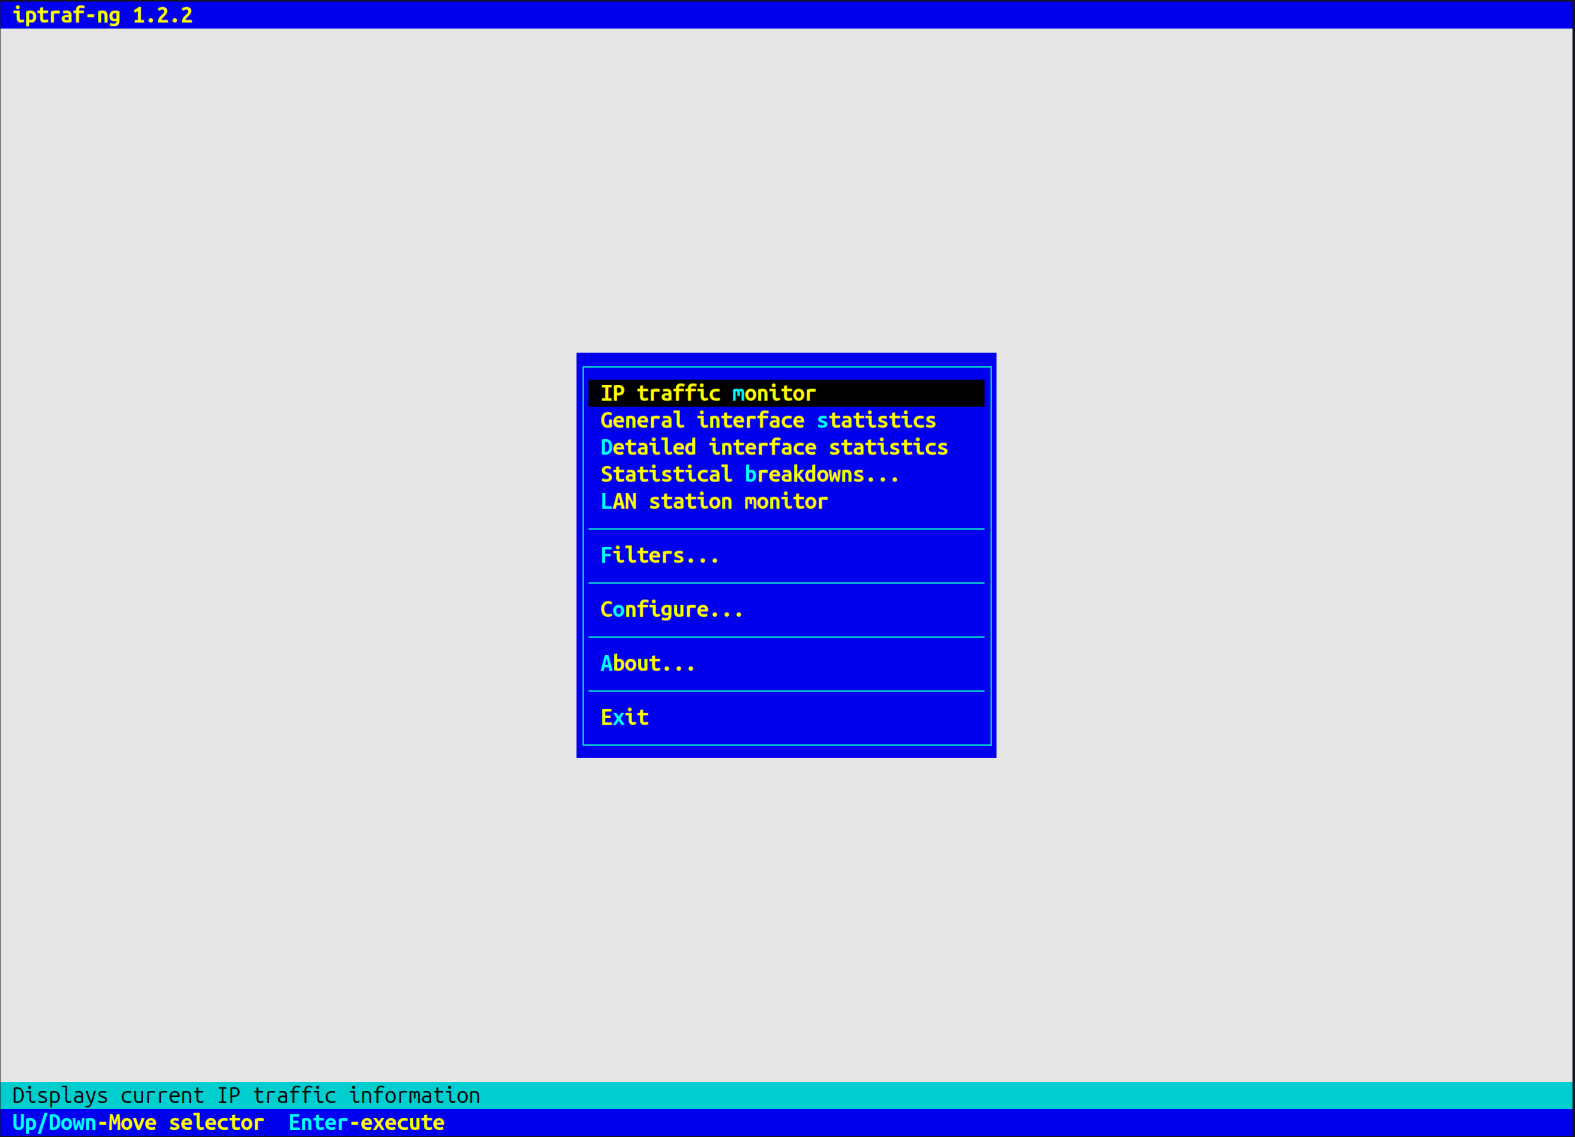
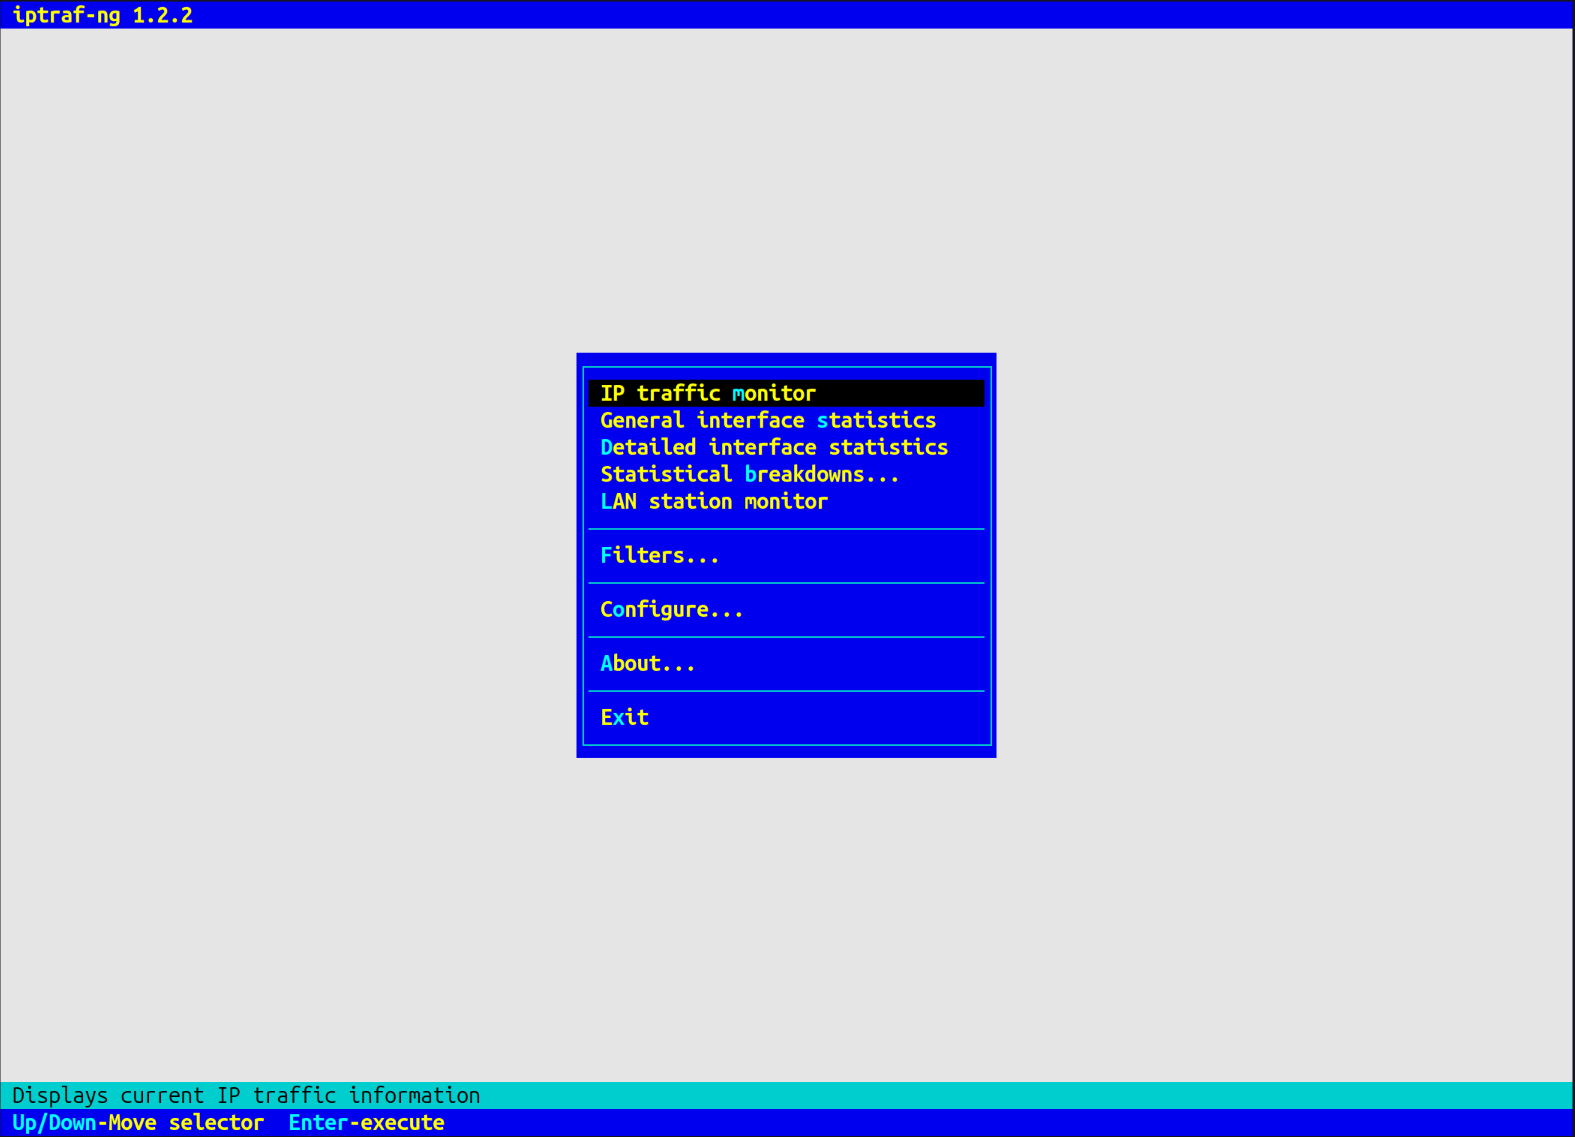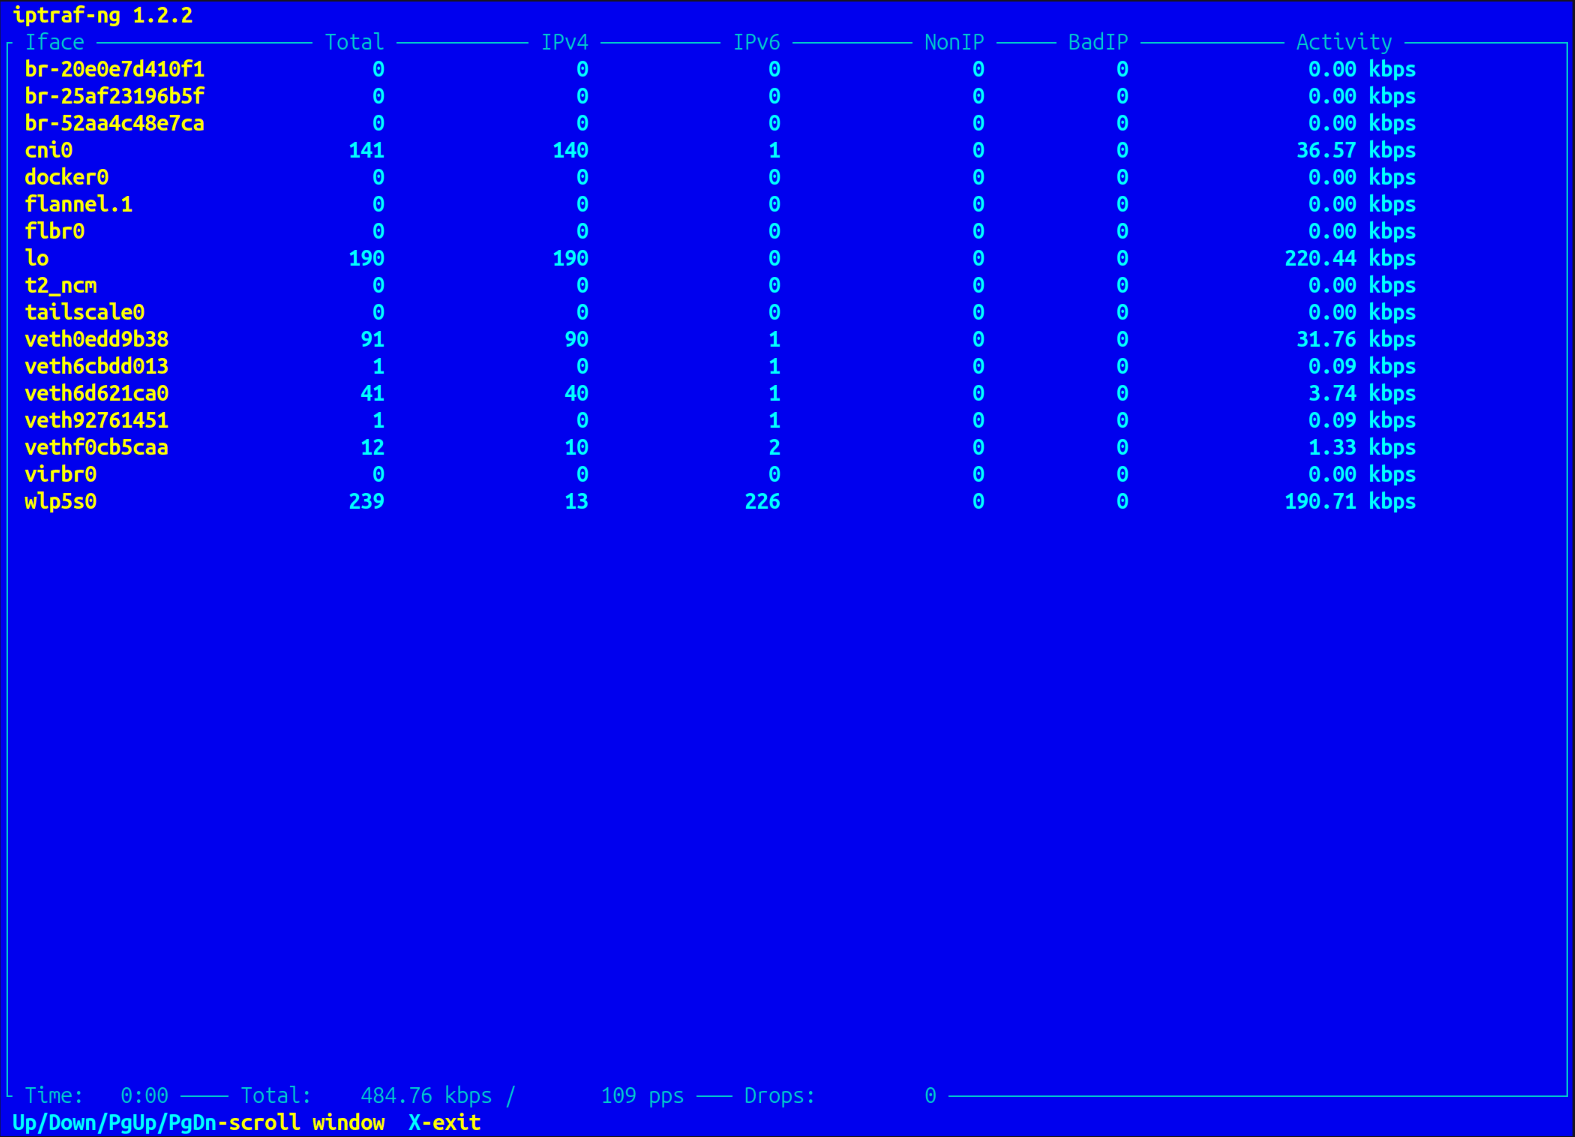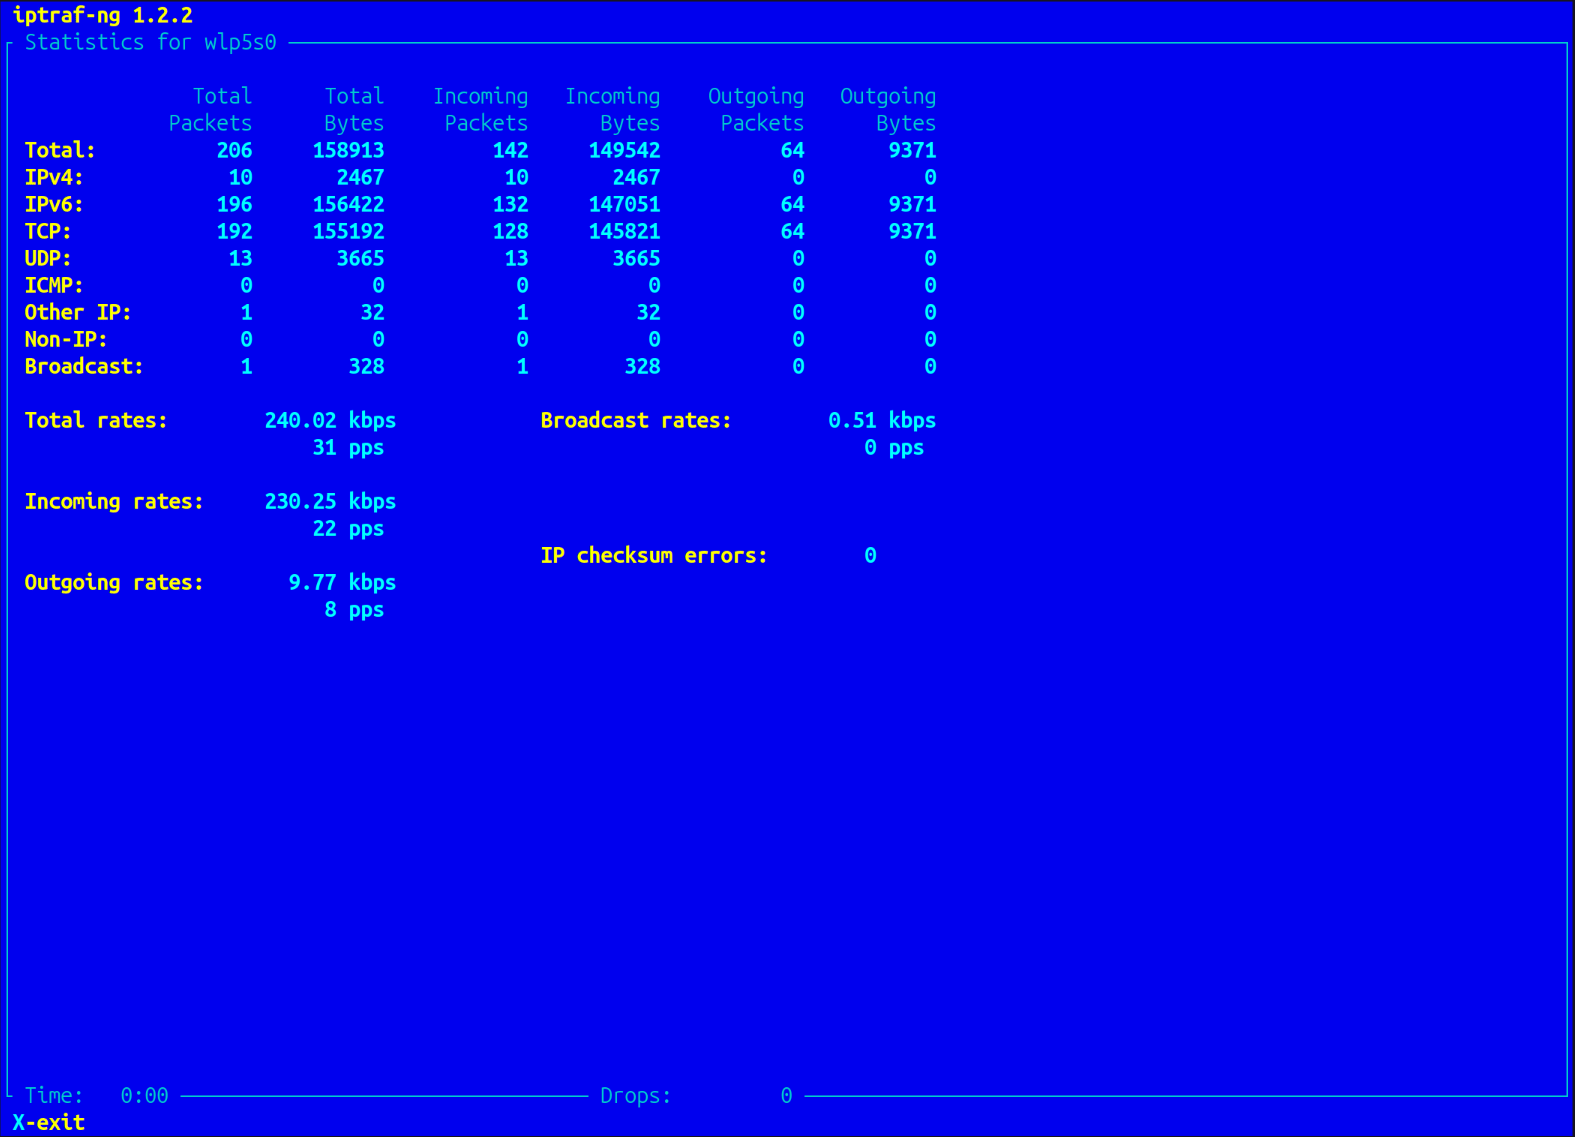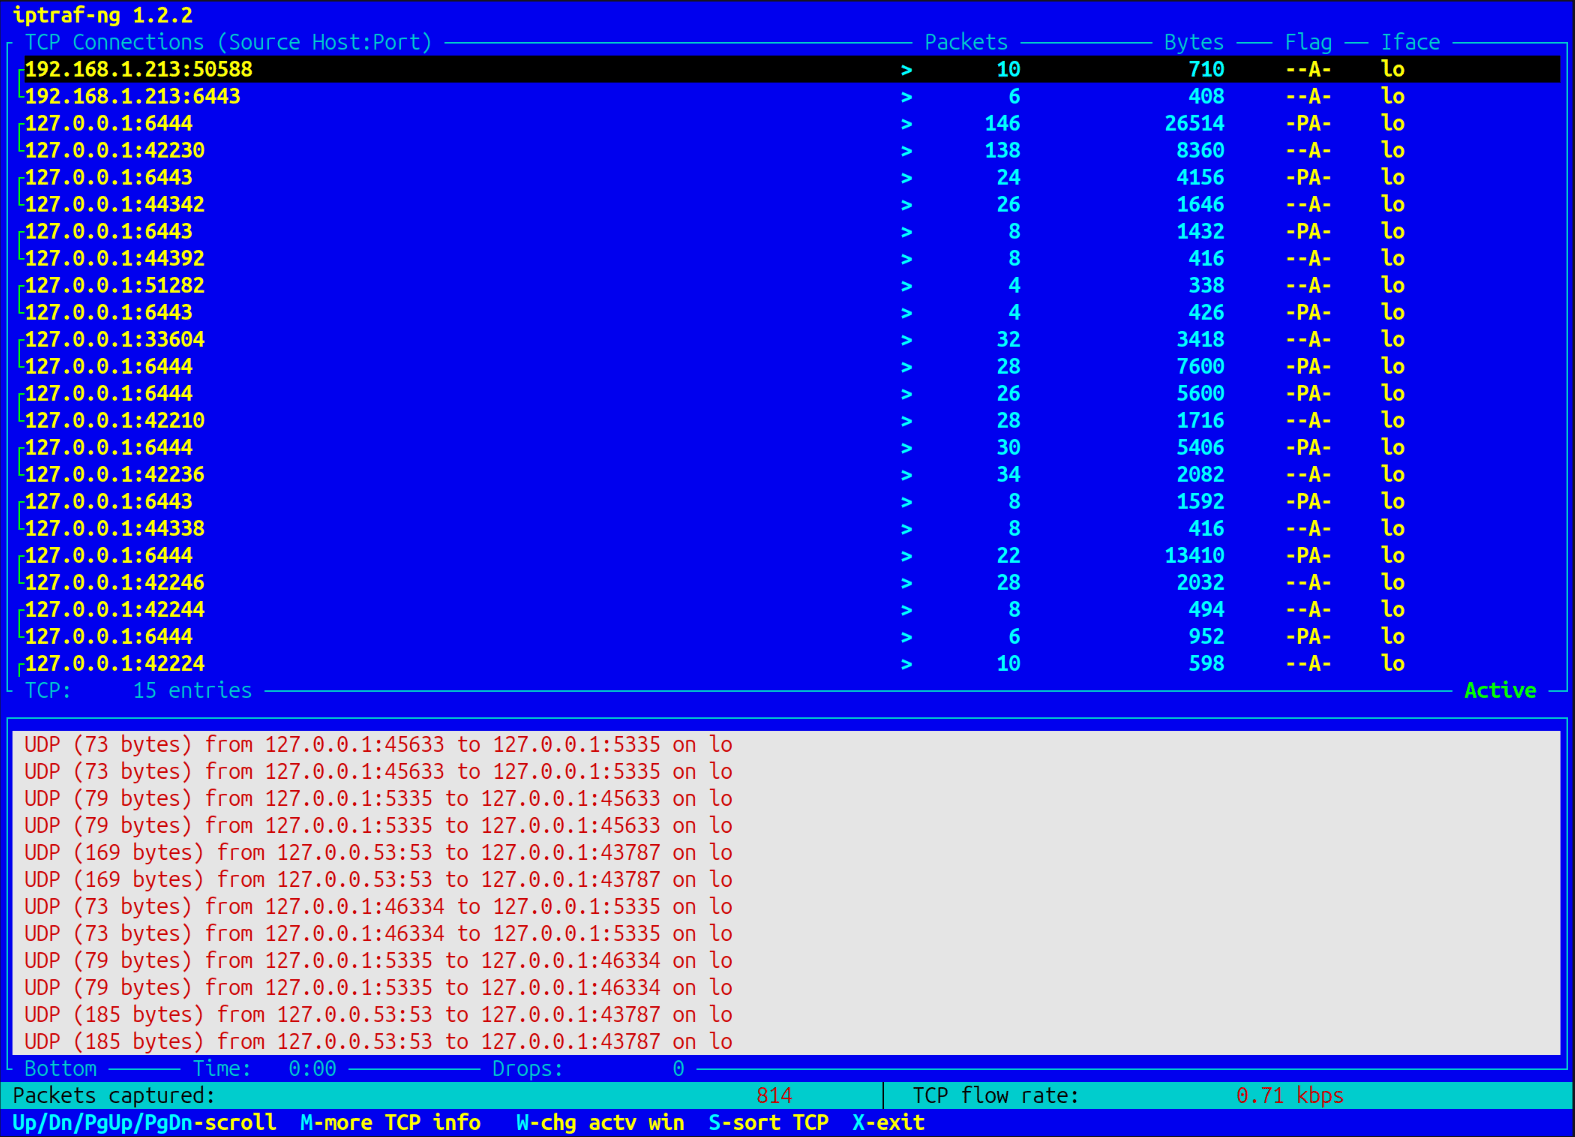
iptraf-ng is a TUI for observing network traffic and connection statistics and TCP traces and advanced low-level monitoring in the terminal.
The built in traffic monitor separates TCP connections from other packets, showing endpoints, byte counts and TCP flags as traffic arrives. Other views group activity by interface, service port, packet size or LAN station to show how traffic is distributed as it is captured live on the machine.
You can choose which interface to listen on and you can filter or restrict the protocols, addresses and ports shown without changing network rules. The tool logs statistics, and command-line options start a chosen monitor in the background for a timed run. Packet capture requires root access.
For Linux system administrators, network engineers, and security engineers can use iptraf-ng for checking busy connections and identifying which hosts or services account for observed traffic.