knife
Share on:
Enter Your Mastodon Instance
Copy the link below to share to Mastodon
https://terminaltrove.com/knife/
A reverse engineering CLI and TUI for PE, ELF and Mach-O binaries.
Script Preview
Review this script before executing in your terminal.
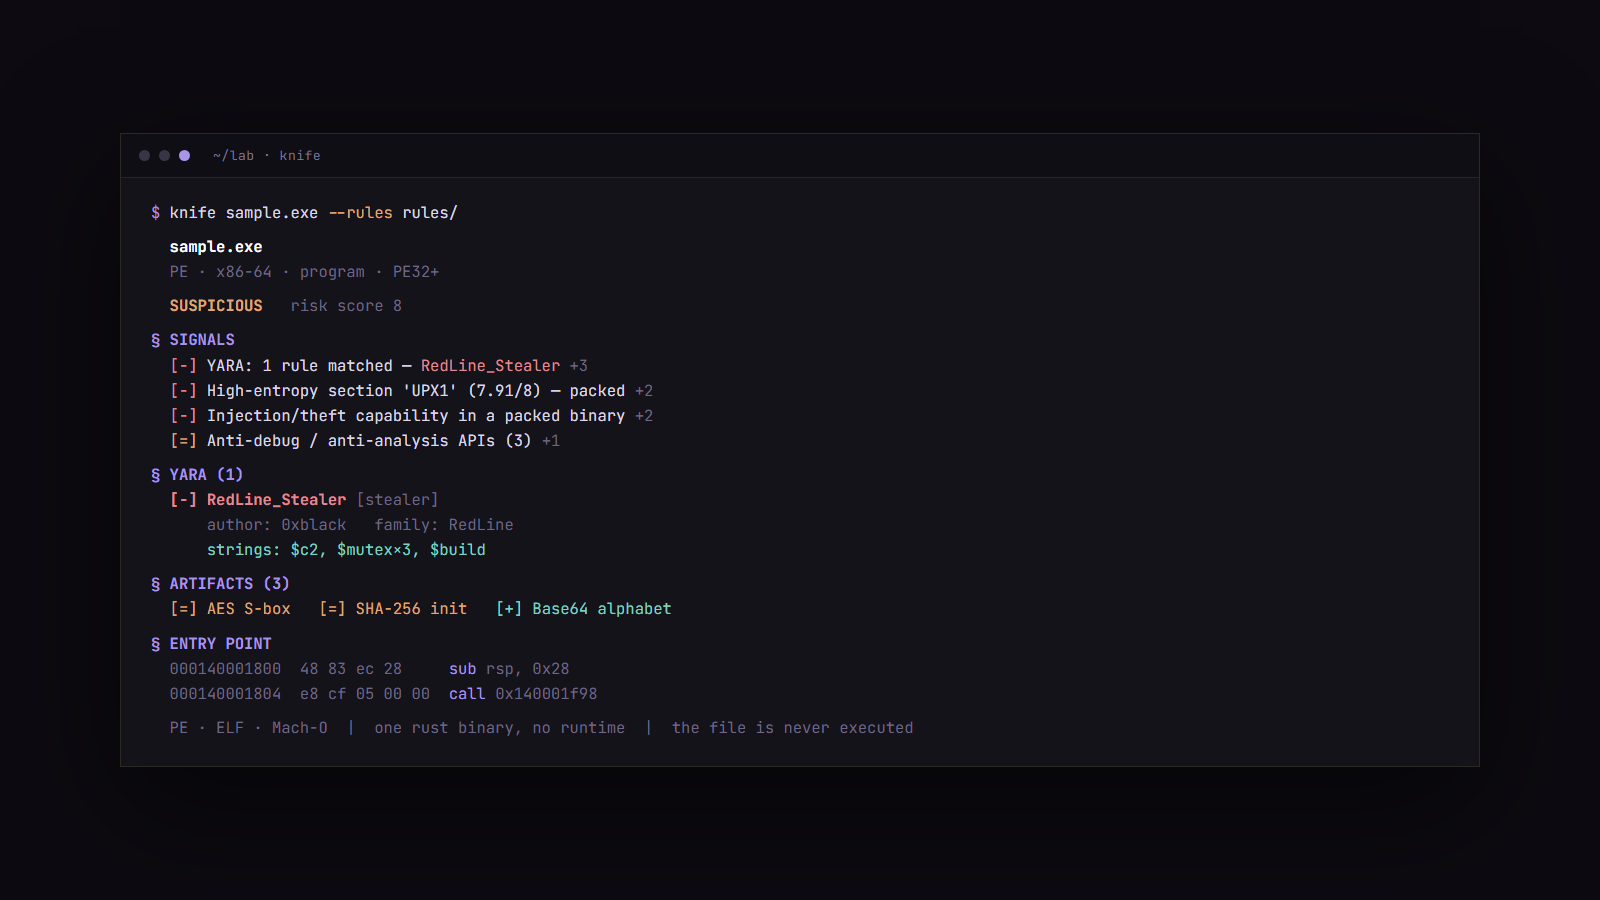
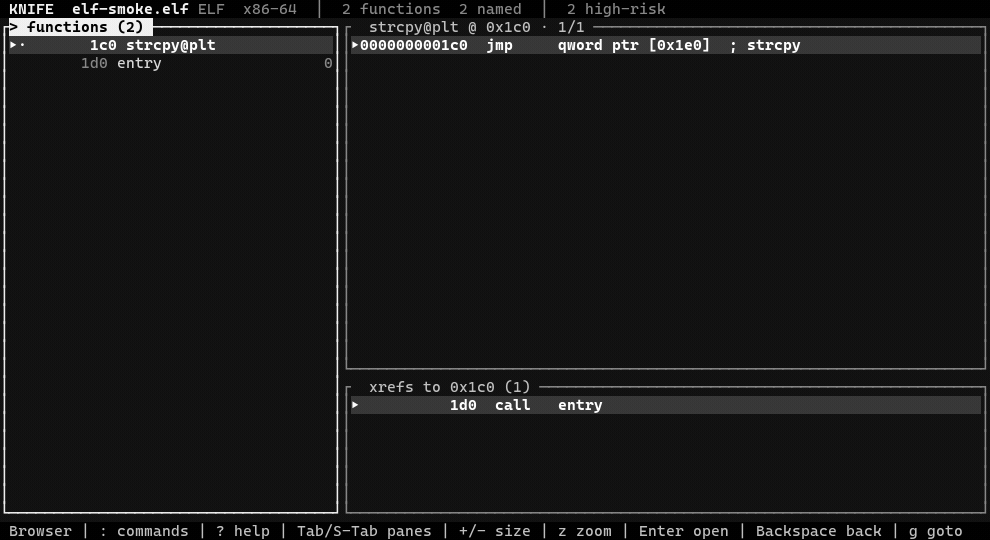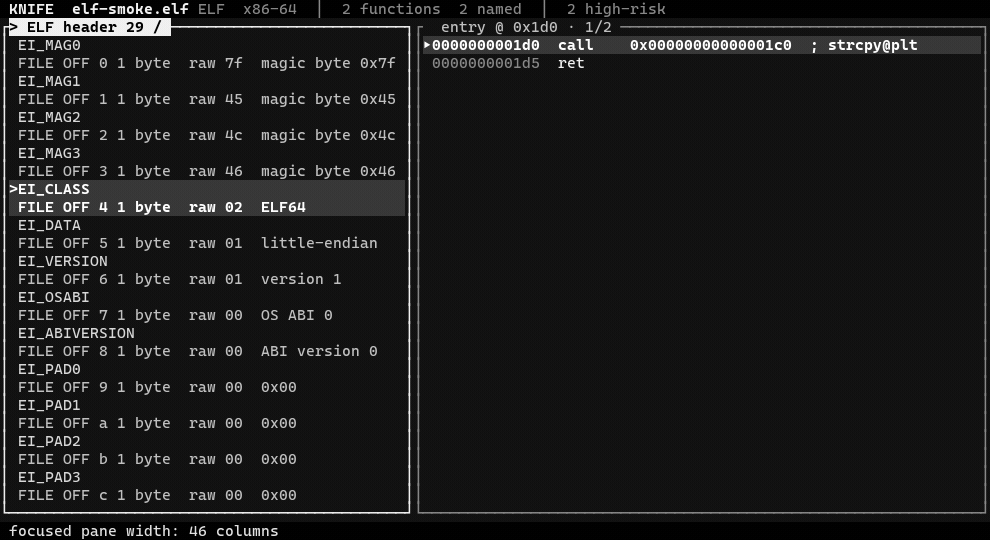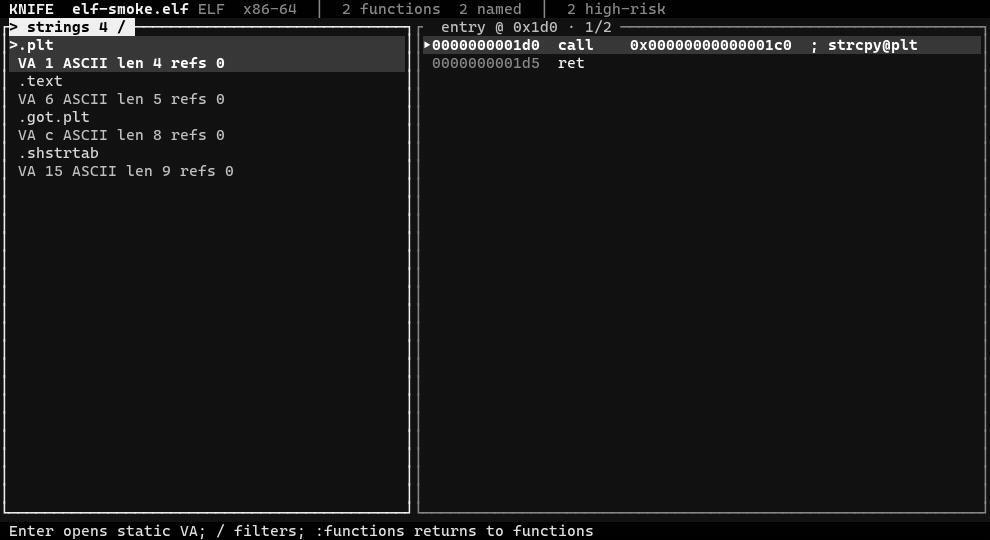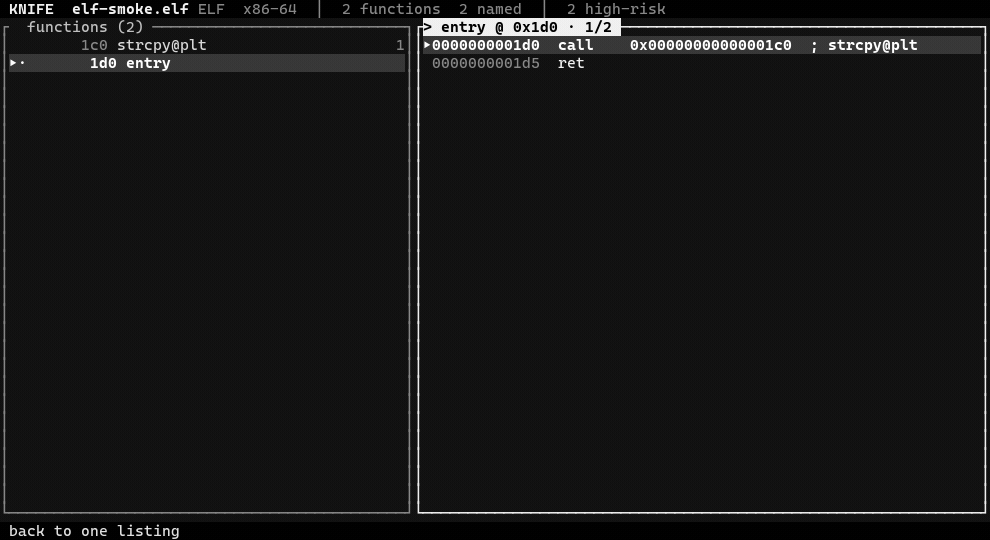
knife is a CLI and TUI for static analysis of PE, ELF and Mach-O binaries.
It reports hashes, imports, strings, indicators, entropy and exploit mitigations. It recovers functions, disassembles code and traces references; it also flags dangerous calls and ranks possible bugs from their arguments.
You can inspect pseudocode and call graphs, save names and notes, compare binaries, or export patched copies. Analysis results are available as JSON.
Security researchers and reverse engineers can use knife to examine unfamiliar executables and drivers through inspection and static analysis in the terminal.


